您现在的位置: 萬盛學電腦網 >> 程式設計 > >> 資料庫 >> MySQL 教學
MySQL 用戶認證核心原理與源碼深度解析
引言:不止於用戶名與密碼
在應用層開發中,身份驗證通常僅涉及 username 與 password 兩個字段。但作為企業級數據庫,MySQL 的認證體系遠比這複雜:它融合了基於主機的訪問控制(Host-based Access Control)、權限矩陣、資源限制 等多維度檢查。本文將從系統表結構、認證流程圖、核心源碼(sql_acl.cc)三個維度,深度剖析 MySQL 登錄認證的完整鏈路。
一、核心系統表:mysql.user 結構解讀
MySQL 將用戶信息、全局權限、資源限制、SSL 憑證等全部存儲在 mysql.user 表中(MySQL 5.7 為例,共 39 字段)。認證階段主要涉及前三列:
| 字段 | 類型 | 說明 |
|---|---|---|
Host | char(60) | 允許連接的主機名/IP,支持通配符 % |
User | char(32) | 用戶名 |
Password | char(41) | 加密後的密碼值(SHA1 雙重哈希) |
關鍵設計:三元組 (Host, User, Password) 共同決定一個合法身份。 同一用戶名可對應不同 Host 記錄,實現「同用戶、不同來源、不同權限」的精細控制。
示例數據解讀
mysql> SELECT Host, User, Password FROM user;
+-----------+------+----------+
| Host      | User | Password |
+-----------+------+----------+
| localhost | root |          |
| 127.0.0.1 | root |          |
| localhost |      |          |
+-----------+------+----------+
- 前兩行:
root用戶僅允許本地連接(localhost/127.0.0.1),密碼為空。 - 第三行:匿名用戶(User 為空),允許本地任意用戶名登錄,但無任何操作權限(僅能
SHOW DATABASES等元操作)。
二、認證流程全景圖
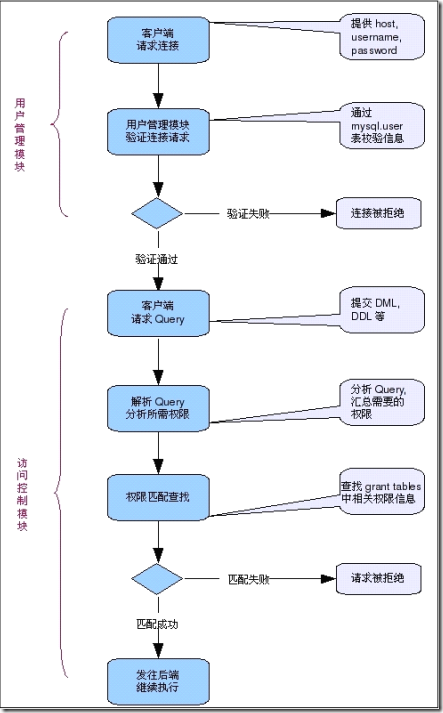
流程核心節點:
- TCP 連接建立 → 獲取客戶端 IP/主機名
- Host 層檢查:
acl_check_host()驗證mysql.user.Host是否匹配 - 用戶層檢查:
check_user()驗證用戶名/密碼 - 權限與資源校驗:連接數、查詢數、更新數、並發限制等
三、核心源碼跟蹤(基於 MySQL 5.6/5.7)
入口函數:login_connection()
static bool login_connection(THD *thd) {
    NET *net = &thd->net;
    int error;

    // 設置連接階段超時
    my_net_set_read_timeout(net, connect_timeout);
    my_net_set_write_timeout(net, connect_timeout);

    // 核心驗證邏輯
    error = check_connection(thd);
    net_end_statement(thd);

    if (error) {
        statistic_increment(aborted_connects, &LOCK_status);
        return true;  // 認證失敗
    }

    // 認證成功,恢復默認超時
    my_net_set_read_timeout(net, thd->variables.net_read_timeout);
    my_net_set_write_timeout(net, thd->variables.net_write_timeout);
    return false;
}
核心驗證函數:check_connection() 簡化邏輯
static int check_connection(THD *thd) {
    // 1. 獲取客戶端 IP/主機名
    char ip[30];
    vio_peer_addr(net->vio, ip, &thd->peer_port);
    thd->main_security_ctx.ip = my_strdup(ip);
    thd->main_security_ctx.host_or_ip = thd->main_security_ctx.ip;

    // 可選:反向 DNS 解析獲取主機名
    if (!(specialflag & SPECIAL_NO_RESOLVE)) {
        thd->main_security_ctx.host = ip_to_hostname(&thd->remote.sin_addr, &connect_errors);
        // 截斷過長主機名,防止溢出
        if (thd->main_security_ctx.host) {
            thd->main_security_ctx.host[min(strlen(...), HOSTNAME_LENGTH)] = 0;
            thd->main_security_ctx.host_or_ip = thd->main_security_ctx.host;
        }
        // 連接錯誤過多導致主機被封鎖
        if (connect_errors > max_connect_errors) {
            my_error(ER_HOST_IS_BLOCKED, MYF(0), thd->main_security_ctx.host_or_ip);
            return 1;
        }
    }

    // 2. Host 白名單檢查
    if (acl_check_host(thd->main_security_ctx.host, thd->main_security_ctx.ip)) {
        my_error(ER_HOST_NOT_PRIVILEGED, MYF(0), thd->main_security_ctx.host_or_ip);
        return 1;
    }

    // 3. 解析客戶端發送的認證包(用戶名、密碼、默認數據庫)
    char *user = end;
    char *passwd = strend(user) + 1;
    uint user_len = passwd - user - 1;
    // ... 省略協議解析細節 ...

    // 4. 用戶名/密碼驗證
    return check_user(thd, COM_CONNECT, passwd, passwd_len, db, TRUE);
}
關鍵子函數職責
| 函數 | 職責 | 失敗返回 |
|---|---|---|
acl_check_host() | 遍歷 mysql.user 表,檢查是否存在匹配的 Host 記錄(支持通配符) | ER_HOST_NOT_PRIVILEGED (1130) |
check_user() | 在通過 Host 檢查的記錄中,進一步匹配 User 與 Password(採用挑戰-響應機制,防重放) | ER_ACCESS_DENIED_ERROR (1045) |
acl_getroot() / get_user_options() | 構建用戶權限上下文,檢查 max_connections、max_user_connections 等資源限制 | 對應資源超限錯誤碼 |
四、認證機制的關鍵特性
1. 基於挑戰-響應的密碼驗證
MySQL 不在網絡上傳輸明文密碼。流程:
- Server 生成 20 字節隨機數(
scramble)發送給 Client - Client 計算:
SHA1(password) XOR SHA1(scramble + SHA1(SHA1(password))) - Server 從
mysql.user.Password讀取SHA1(SHA1(password)),用相同算法驗證
2. 插件化認證框架(MySQL 5.5+)
通過 plugin 表註冊認證插件(如 mysql_native_password、caching_sha2_password、auth_socket、LDAP、Kerberos 等),實現可插拔認證方式。
3. 主機名緩存與 FLUSH HOSTS
為避免頻繁 DNS 解析,MySQL 維護內存主機緩存。當 max_connect_errors 觸發封鎖時,需執行 FLUSH HOSTS 或重啟服務解封。
五、安全加固建議
- 禁用匿名用戶:
DROP USER ''@'localhost'; - 限制 root 遠程登錄:僅保留
root@'127.0.0.1'和root@'localhost' - 強制使用強密碼:配置
validate_password插件 - 啟用 SSL/TLS:防止中間人攻擊竊取挑戰-響應數據
- 設置合理的
max_connect_errors:防止暴力破解導致誤封合法主機
總結
MySQL 認證並非簡單的「查表比對」,而是一個分層、可擴展、狀態感知的安全子系統:
- Host 層 實現網絡層面的首道防線
- User/Password 層 通過加密挑戰-響應確保憑證不落地傳輸
- 權限/資源層 在認證成功後進一步約束會話能力
理解這一機制,不僅有助於排查「Access denied」類故障,更是設計數據庫安全架構、實現自定義認證插件的基石。
- 上一篇程序編程: MySQL 百萬級數據插入性能測試:存儲過程 vs LOAD DATA 實戰對比
- 下一篇程序編程: MySQL RAND() 隨機查詢性能陷阱與高效替代方案實測
推薦文章
- MySQL REGEXP 正則表達式完整語法與實戰速查
- PHP MySQL SELECT 查詢完整教學:結果集處理、HTML 表格輸出與…
- SQL 查詢與刪除重複記錄完整實戰 (含游標法、臨時表法)
- MySQL 開啟遠程訪問三種方法:GRANT、修改 host、配置 bind-a…
- MySQL 鎖機制全景解析:表鎖、頁鎖、行鎖與死鎖應對
- SQL Server 2008 Express 開啟遠程訪問完整圖解
- MySQL mysqldump 命令詳解:從備份到遷移的完整指南
- MySQL CONCAT 遇 NULL 回傳 NULL?教你三招徹底解決字串串接…
- SQLite Database Browser 2.0 圖文教學:建庫、建表、編…
- MySQL 連線逾時徹底解決:wait_timeout 配置優化與連線池最佳實踐
copyright © 萬盛學電腦網 all rights reserved